What would make you click on an advertisement for an unfamiliar crypto exchange service?
For one Korean employee living in the US, the answer was simple: a better exchange rate.
The service advertised a rate about 2–3% better than competing options. He needed to sell his USDT and send money to Korea, so the offer seemed worth investigating.
There was nothing obviously absurd about it.
He clicked the Instagram ad and began the exchange. The website then asked him to complete an AML check before continuing. He connected his USDT account and approved the transaction.
He lost approximately $25,000.
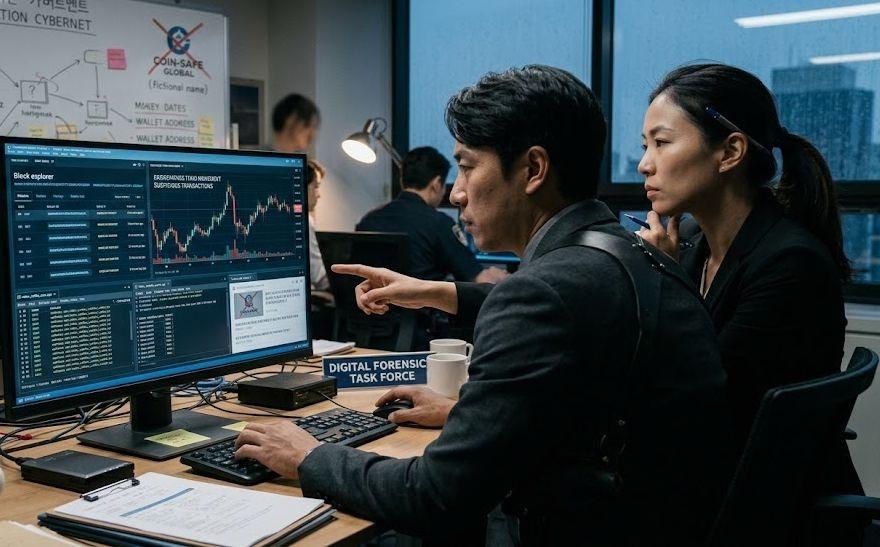
A private cyber investigation later revealed that the scam was more sophisticated than a fake website with a convincing design. It also highlighted several assumptions that can make online fraud harder to recognize and investigate.
A scam doesn't have to look like a scam
The first mistake is assuming that scammers need to make extraordinary promises.
They don't.
An exchange rate that is slightly better than everyone else's can be more effective than an outrageous offer. It gives the victim a plausible explanation: perhaps this company has lower costs, better liquidity, or simply wants to attract customers.
The offer doesn't need to look impossible.
It only needs to look good enough to click.
That's why an unfamiliar service offering consistently better terms than established competitors deserves scrutiny. The important question isn't just whether the deal is attractive. It's why the company can afford to offer it.
The AML check made the scam more believable
The next step was particularly effective because it borrowed credibility from a legitimate financial process.
The website asked the victim to complete an AML check.
There's nothing strange about that on its own. Real financial services conduct AML and compliance checks.
But this wasn't really a security check. It was part of the mechanism used to convince the victim to authorize the transaction that emptied his account.
A genuine AML process is intended to establish whether funds are legitimate and where they came from. It isn't supposed to require the customer to send those funds away as proof.
In other words, the scam didn't invent a fake concept. It took a real concept and put it inside a fraudulent workflow.
Behind the website was an entire ecosystem
The investigation eventually connected the incident to a Drainer-as-a-Service operation.
That's a useful example of how online fraud has become more modular.
The person running the scam doesn't necessarily need to build the infrastructure.
One group can provide fake websites, payment-draining tools, and administrative systems. Affiliates can rent the infrastructure, purchase advertising, find victims, and take a share of the proceeds.
Some publicly known cases have reportedly allowed affiliates to keep up to 80%.
This also creates a problem for investigators. The person responsible for the advertisement may not be the person who built the website. The advertiser's account may not even have been funded with their own money.
In this case, the advertising trail potentially led nowhere because the campaign could have been paid for with a stolen card.
Further investigation into the transactions revealed P2P traders suspected of helping turn the stolen funds into cash.
Why finding one Instagram ad can be surprisingly difficult
The investigators needed to see the advertisement themselves.
That sounds easy until you consider how targeted advertising works.
Two Instagram users can open the same app at the same time and receive completely different advertisements.
Location, age, interests, device, and account history can all affect what appears.
A campaign targeting people in the US might therefore be invisible to investigators accessing Instagram from somewhere else.
There was another problem: cloaking.
Some fraudulent campaigns don't show everyone the same landing page. A user who matches the campaign's targeting conditions may receive the real scam site, while other visitors see something harmless.
So the investigators had to create an account that looked like the kind of account the scammers were targeting.
They created a fresh email address, used a consistent browser profile, and connected through a US IP address. Instagram also required a US phone number.
A foreign number would have made the account less consistent with the target profile. VoIP numbers can be rejected, and public SMS websites are unsuitable because their verification codes can be seen by anyone.
The team used a temporary US mobile number to activate the account.
Then they waited.
They followed financial and investment pages similar to those associated with the victim and used the account like an ordinary person.
Eventually, the P2P exchange advertisement appeared.
An advertisement can disappear before an investigation is finished
Once the ad appeared, the priority changed from finding it to preserving it.
Scam advertisements can disappear quickly. The investigators captured screenshots and recorded the advertisement ID, advertiser ID, landing page URL, and timestamps.
They also generated file hashes so they could later demonstrate that the evidence had not been altered.
Just as importantly, they avoided turning assumptions into facts.
A shared payment account doesn't prove that two accounts belong to the same person. A person who received or converted stolen funds isn't automatically proven to be part of the original scam.
That may sound obvious, but investigations can become unreliable when every connection is treated as proof of identity or intent.
The tools were easy. Staying invisible was hard.
The technical setup wasn't particularly exotic.
Residential IP addresses and a clean browser were relatively straightforward to obtain. It was also easy to receive verification SMS online to a temporary number.
The challenge was behavioral.
The investigative account had to behave naturally enough to receive the right advertising without doing anything that would cause Instagram to restrict or remove it.
There was no guarantee of success.
And there is an unavoidable gray area: an account created for a legitimate investigation can still violate a platform's terms of service.
Even after finding the advertisement, investigators couldn't simply make the stolen money come back. A private cyber investigation team cannot freeze bank accounts or issue subpoenas.
Its role is to collect and preserve evidence and pass it to parties that have the authority to act.
That can mean the platform itself, a lawyer, a payment provider, a court, or law enforcement.
For ordinary users, however, none of this needs to be complicated.
A slightly better exchange rate isn't proof of fraud.
An AML check isn't proof of legitimacy.
And if an unfamiliar financial service asks you to authorize a transaction to prove that your money is clean, that's the point where you should stop.